News World
What your coding agent sends home
Hello,
This issue asks a question nobody asks: when your coding agent works, what exactly does it send to the provider's servers? The problem of the week gives three rules and one tool to see what leaves.
Releases
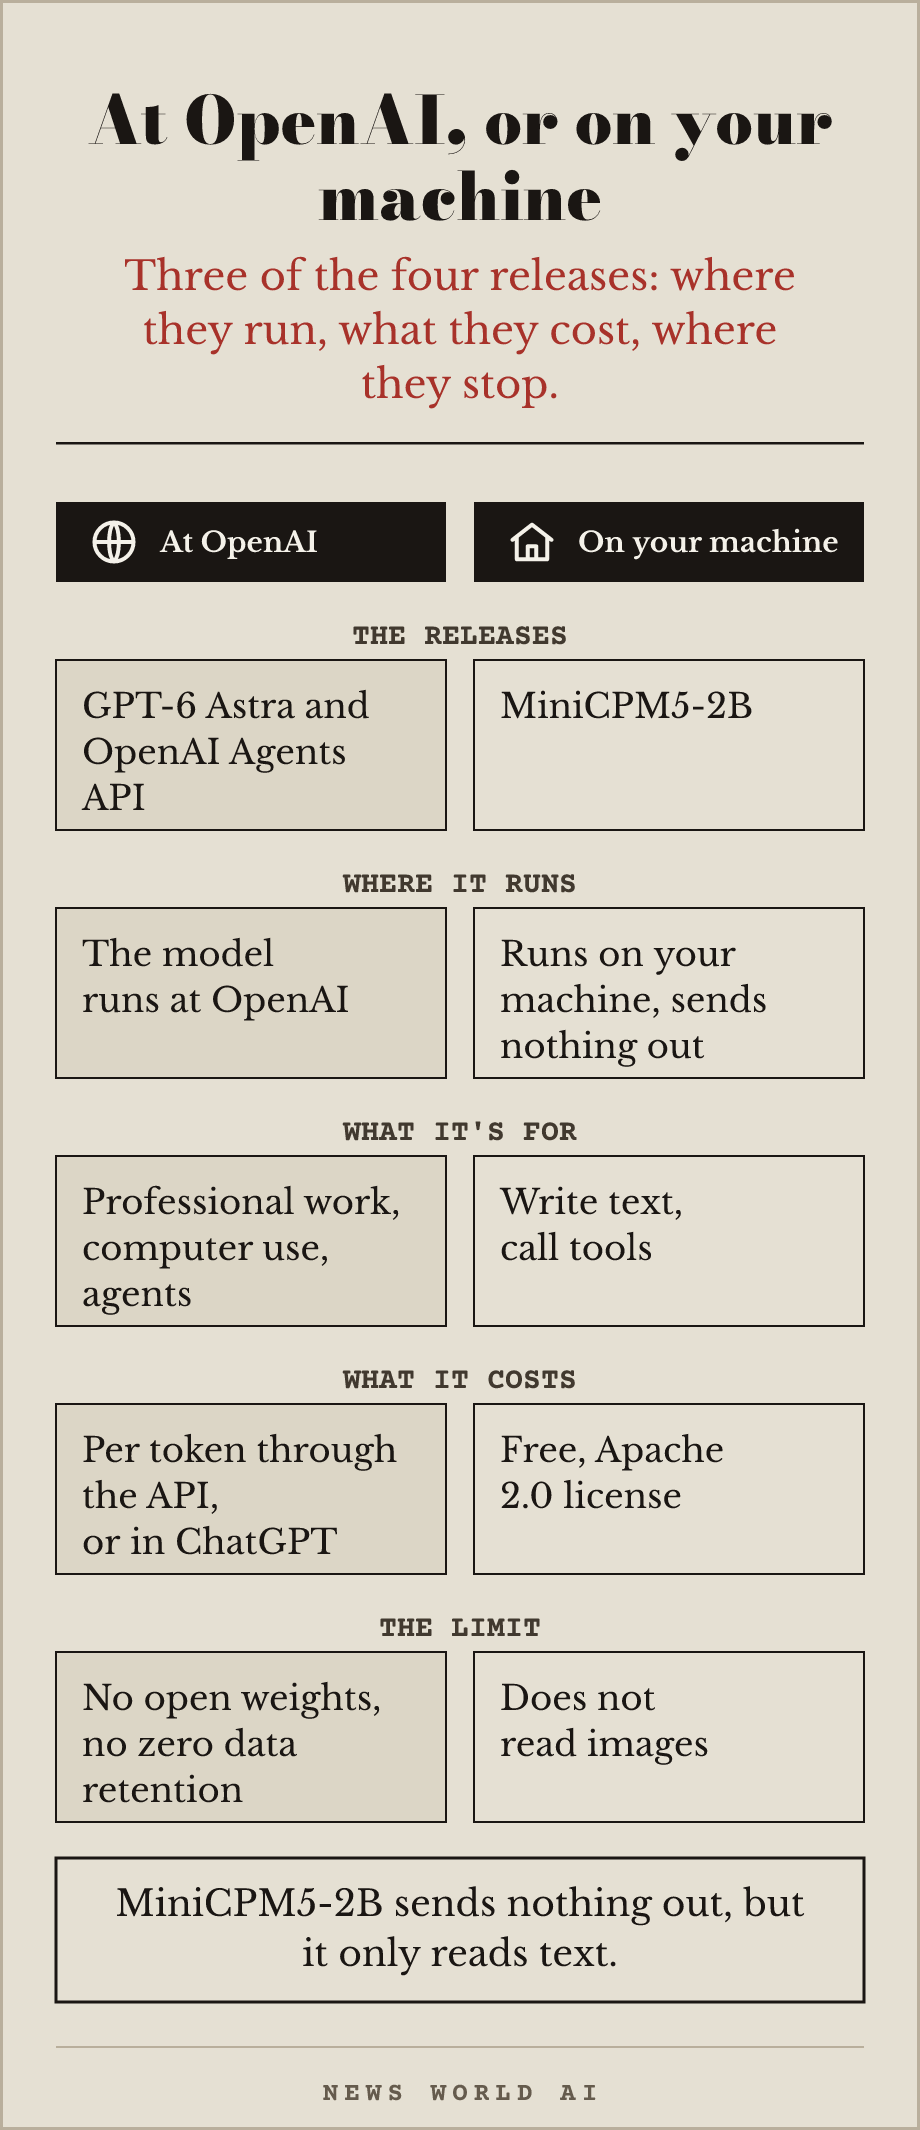
GPT-6 Astra
In ChatGPT Work, in Codex and through the API, from $10 per million input tokens and $50 per million output tokens.
What it's for What OpenAI presents as its most capable model, aimed at professional work: computer use, web browsing, software engineering, cybersecurity, science. On September 8, OpenAI published a proof that it says settles the Navier-Stokes problem (the equations that describe how fluids flow), one of the seven Millennium Prize Problems. It comes from an unreleased internal model that OpenAI says is significantly more capable than GPT-6 Astra. Mathematician Tristan Buckmaster (NYU), who was working on the same approach, disputes OpenAI's account of how the effort started.
The limit No open weights, no version you can host yourself.
OpenAI Agents API
In public beta since September 10. No extra fee: model tokens and tools at standard API rates, plus container time if OpenAI hosts the workspace.
What it's for Build agents whose engine (the loop that moves the agent forward and keeps its session) runs at OpenAI, with a workspace hosted by OpenAI, by a partner or on your own machines, sessions that last several days, tools, and subagents working in parallel. The engine is the one behind Codex (OpenAI's coding agent). Released the same day as GPT-Live-1 in the API, which listens and speaks at the same time.
The limit No zero data retention, no data residency outside the United States.
Suno v6
v6-mini for everyone, v6 and v6-wild for Pro and Premier subscribers.
What it's for Generate music from a text description, to add a soundtrack to content produced by your agent (video, podcast, presentation). A new generation of models developed with industry partners including Warner Music Group, BMG and Believe; older models will be retired. The next day, ElevenLabs and Universal Music Group announced a licensed platform, still in development, where fans will be able to remix tracks by participating artists.
The limit No v6 or v6-wild on the free plan, only v6-mini.
MiniCPM5-2B
42,289 downloads, 1,135 likes on Hugging Face. Apache 2.0 license.
What it's for Write text and call tools with a 2.5-billion-parameter model that runs on your machine without sending anything out. Official lighter builds exist for llama.cpp, Ollama, LM Studio and Macs (MLX).
The limit Does not read images, and no more than 131,072 tokens at a time.
Repos
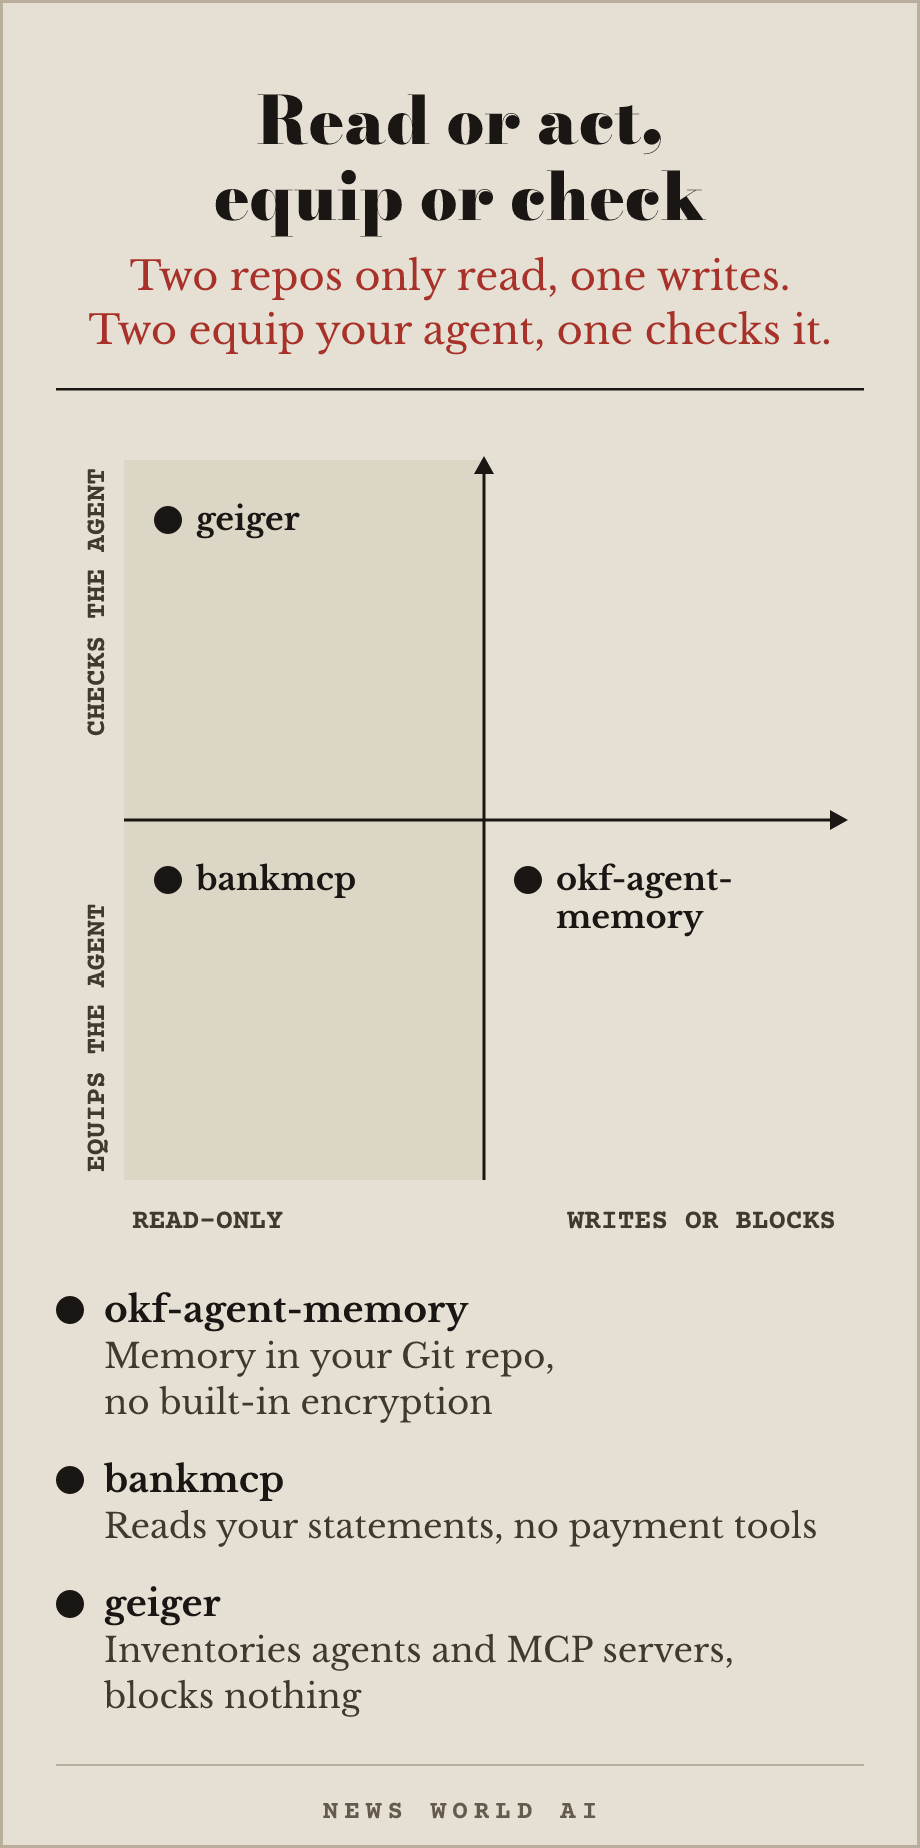
okf-memory/okf-agent-memory · 552 stars · MIT · last commit 9 September 2026
Persistent memory for coding agents, kept in your Git repo as text files. Claims search in under 300 microseconds, ships an MCP server, and claims 80% fewer tokens in its own benchmark. What it does not do: no built-in encryption (everything is plain text), no conflict handling when two agents write at the same time, no remote shared memory yet.
noskillish/bankmcp · 178 stars · MIT · last commit 8 September 2026
A self-hosted, read-only MCP server that queries your own bank accounts via open banking (the set of standards that let authorised software access your accounts), through Enable Banking. Tested with Claude and Claude Code, and experimentally with local models via Ollama. Your agent can read your statements: the server has no payment tools. What it does not do: no payments, no bank outside Enable Banking's network, one user per server, no hosted version.
Atomburstofficial/geiger · 106 stars · MIT · last commit 10 September 2026
A read-only command that inventories the AI agents, MCP servers, extensions and hooks found in known configuration locations. It answers a question most people cannot: what runs on this machine, and what can it reach? What it does not do: does not monitor continuously, does not block anything, does not tell you what an agent actually did.
In brief
NSA, CISA and FBI name six Chinese companies copying US models at industrial scale (DeepSeek, Moonshot AI, Alibaba, MiniMax, StepFun and Z.AI): they query them massively, through proxies and fraudulent accounts, to extract their capabilities. The agencies urge US AI companies to strengthen detection. cisa.gov/news-events/…
Meta presents Muse, a personal agent that browses the web for you. It books appointments for you, and an email or a purchase waits for your approval. Free, within a usage limit. ai.meta.com/muse
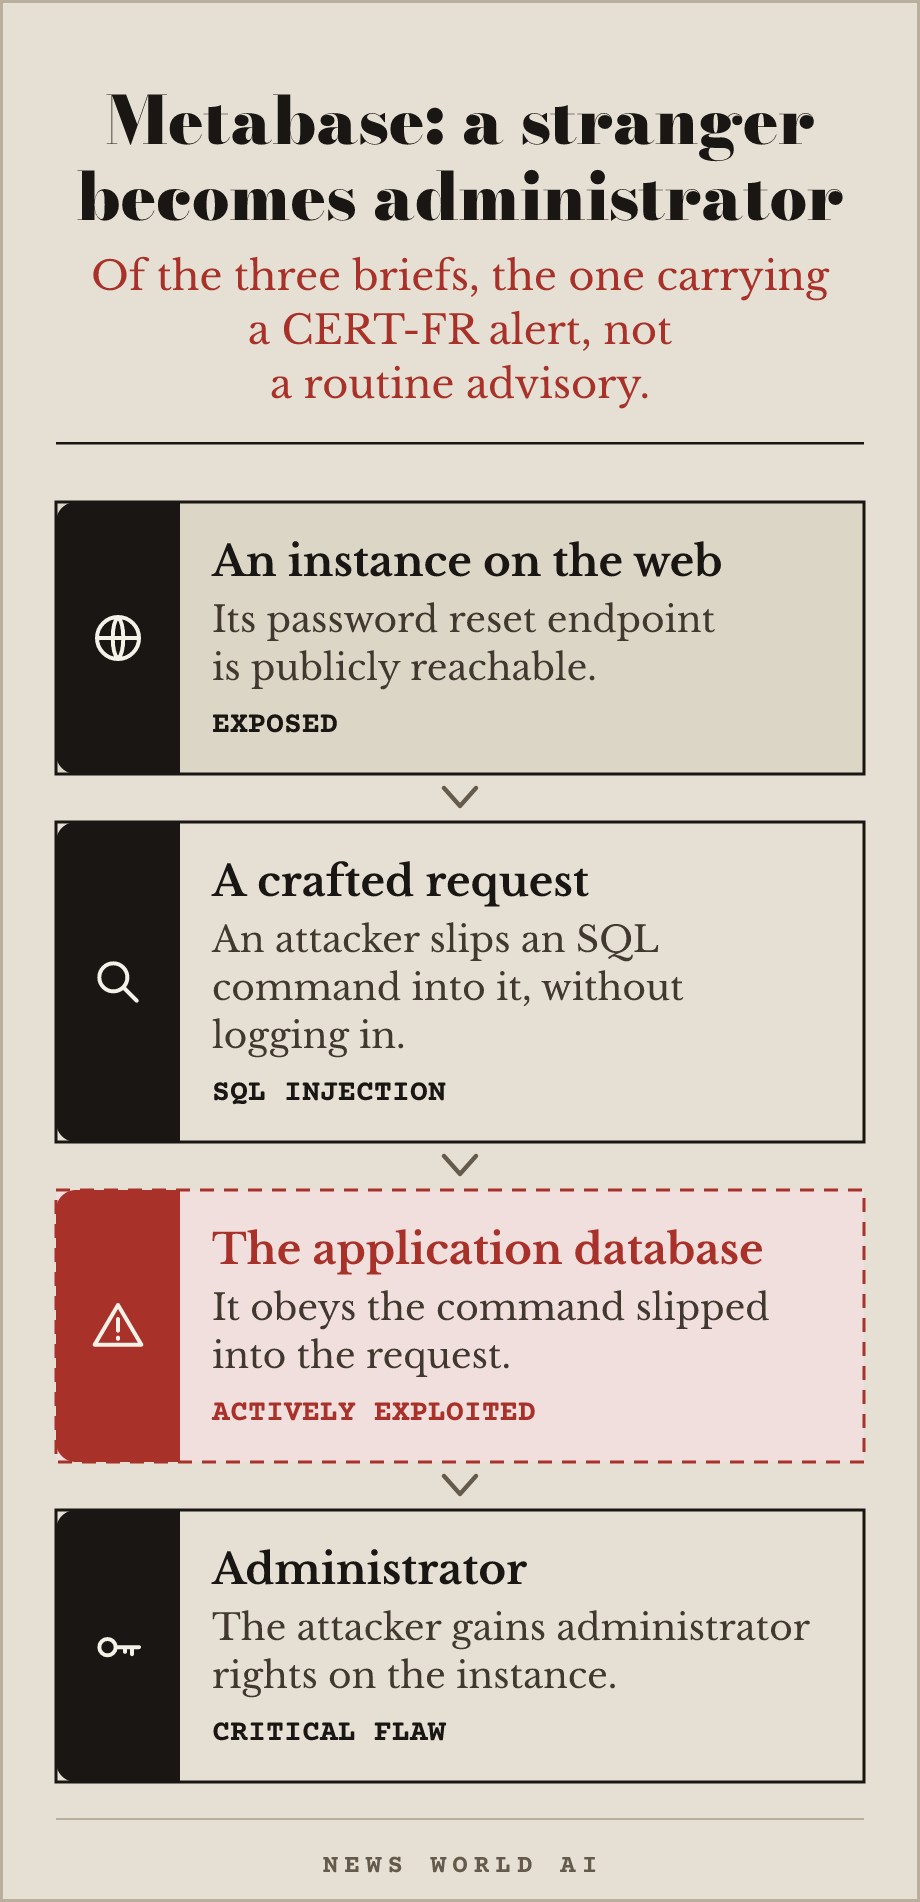
Metabase: a critical SQL injection (CVE-2026-72898) lets an unauthenticated attacker gain administrator rights. CERT-FR issued a full alert, not a routine advisory, on September 10, and is aware of numerous compromises. Install version 0.63.10 or later (1.63.10 for Enterprise; on older branches, 0.58.28, 0.59.25, 0.60.21, 0.61.15 or 0.62.13), or else block public access to /api/session/reset_password. cert.ssi.gouv.fr/alerte/…
The problem of the week
What your coding agent sends without telling you
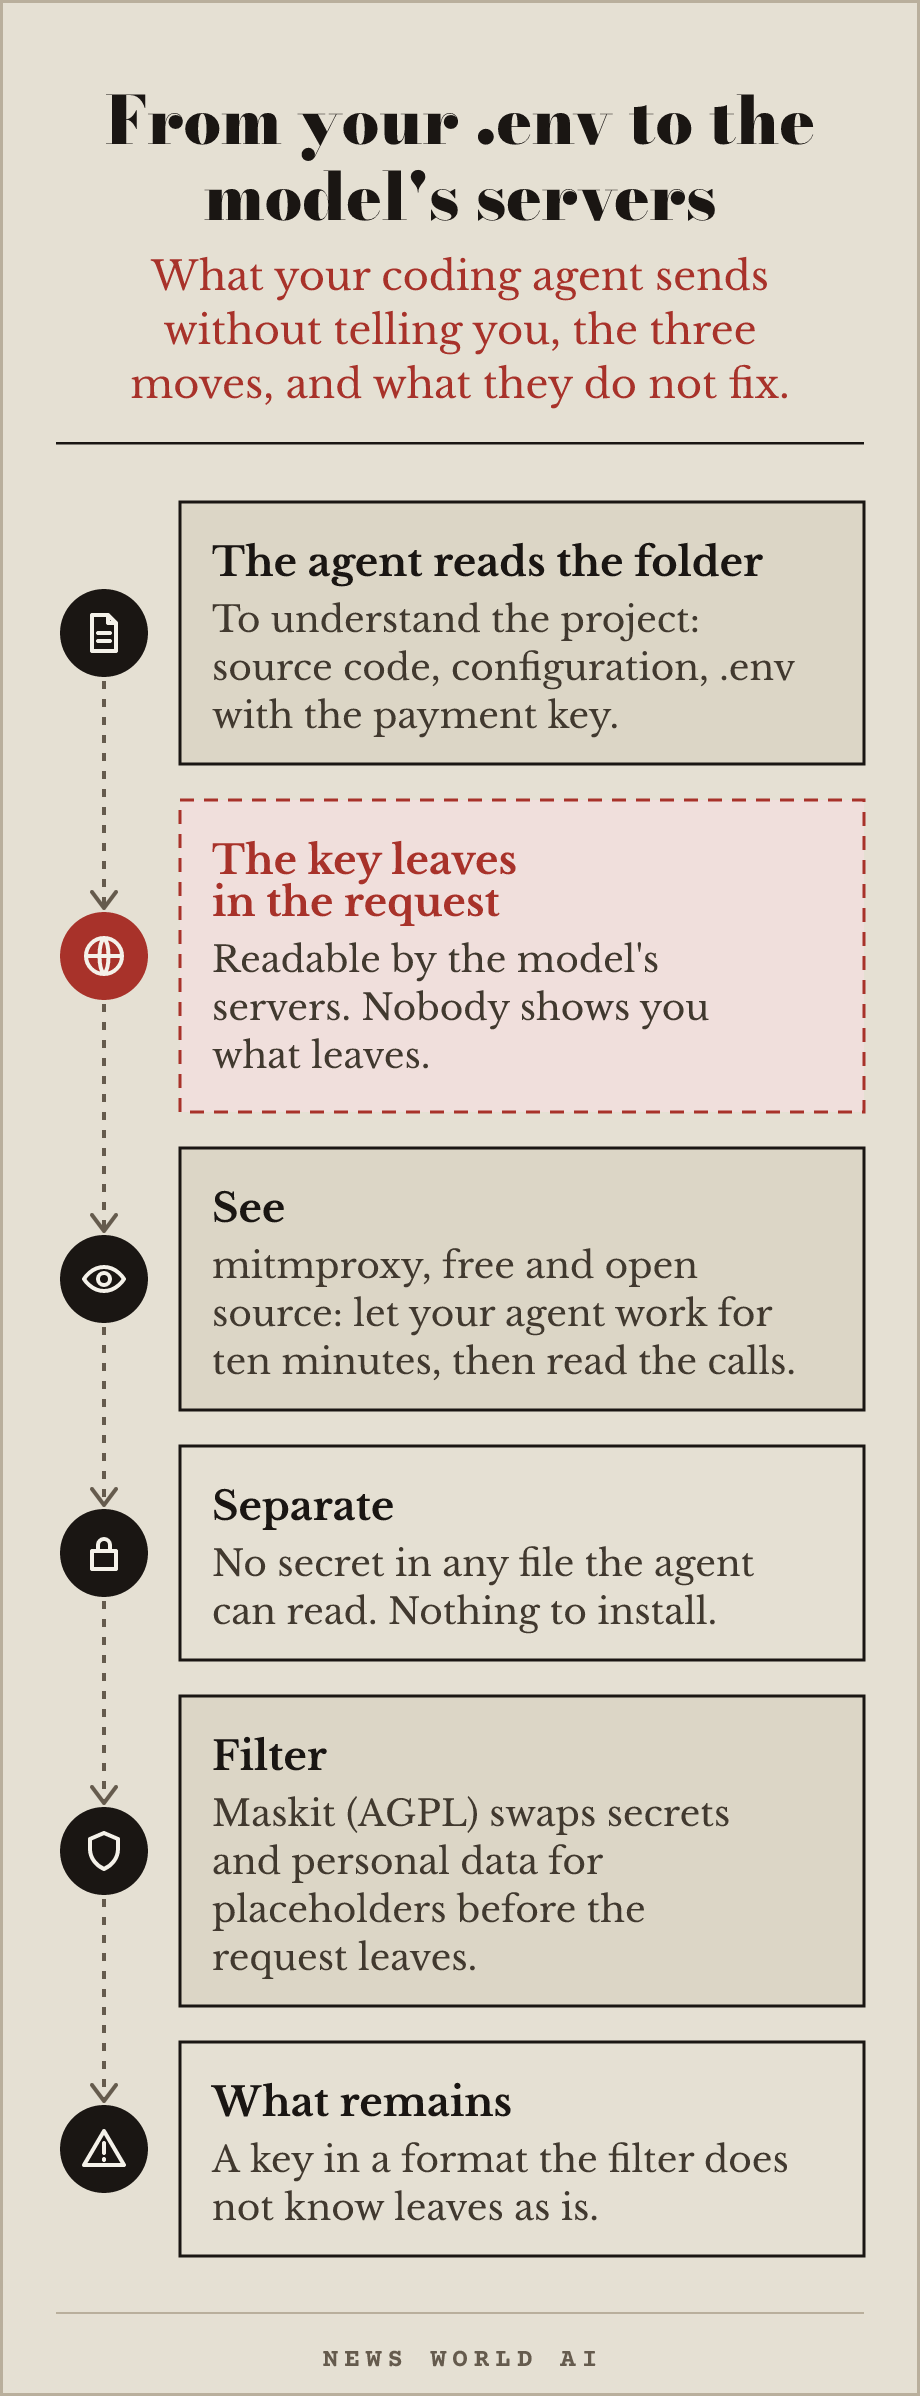
Every time your coding agent works, it sends the provider the contents of the files it reads: your source code, your configuration files, sometimes your environment variables and your keys. You do not see what leaves, because nobody shows you.
Take an example. You have a project with a .env file that holds the key to your payment provider. Your agent reads the folder to understand the project, and the key leaves in the request, readable by the model's servers.
The fix is three steps. First, see what leaves: install a local relay that shows every outgoing request (mitmproxy is free and open source), let your agent work for ten minutes, and read what the calls contain. Second, separate: secrets (keys, passwords, access tokens) must never sit in a file the agent can read. A .env file in the same folder as your code can leave with the rest. Third, filter: Maskit (AGPL license), released this week, sits between your agent and the provider, swaps the secrets and personal data its rules recognise for placeholders, then puts them back in the answer.
List every file in this project that the coding agent can read, identify those that contain secrets, keys or personal data, and propose an exclusion file so the agent never sees them.
What this does not fix: a filter only masks what its rules recognise. A key in a format it does not know, pasted inside a function, leaves as is. The only remedy there is to never write a secret in the code.
mitmproxy to see what leaves.
Worth reading
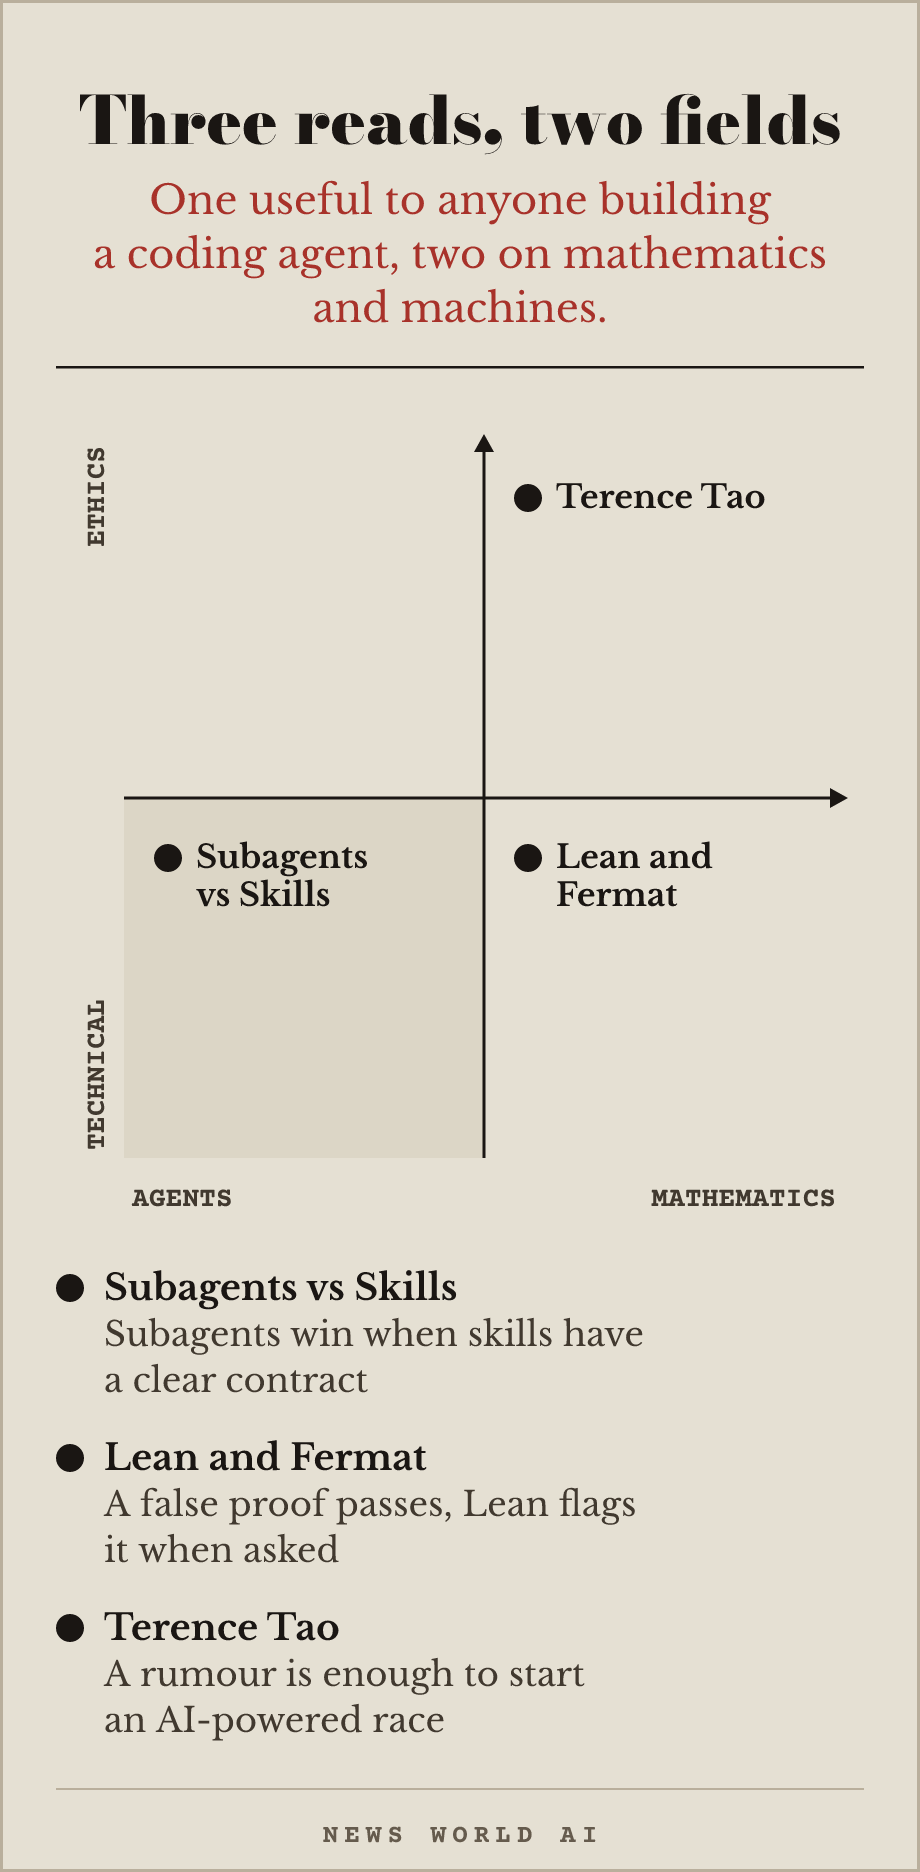
Subagents vs Agent Skills: Executing Reusable Knowledge for Long-Horizon Agentic Tasks · Compares two ways of running the same skill packages: loading their instructions into the agent's context, or handing them to subagents that start from a fresh context. Subagents win when the skills have well-defined inputs and outputs, at the cost of extra coordination tokens. arxiv.org/abs/2609.09233
A "proof" of Fermat's Last Theorem that fits the margin · Trail of Bits shows a bug in Lean, the tool that checks mathematical proofs by machine, sitting in its compiled code rather than its kernel: it lets a false proof of Fermat's Last Theorem through. Lean still flags the extra assumption when asked, and the fix ships in version 4.34.0-rc1. blog.trailofbits.com/2026/09/09/…
Terence Tao on open problems mined by AI · The mere rumour that someone is working on a problem can trigger a massive AI-powered effort to solve it first. Tao worries that researchers may then stop sharing their leads, against centuries of open science. mathstodon.xyz/@tao/…
The security reflex
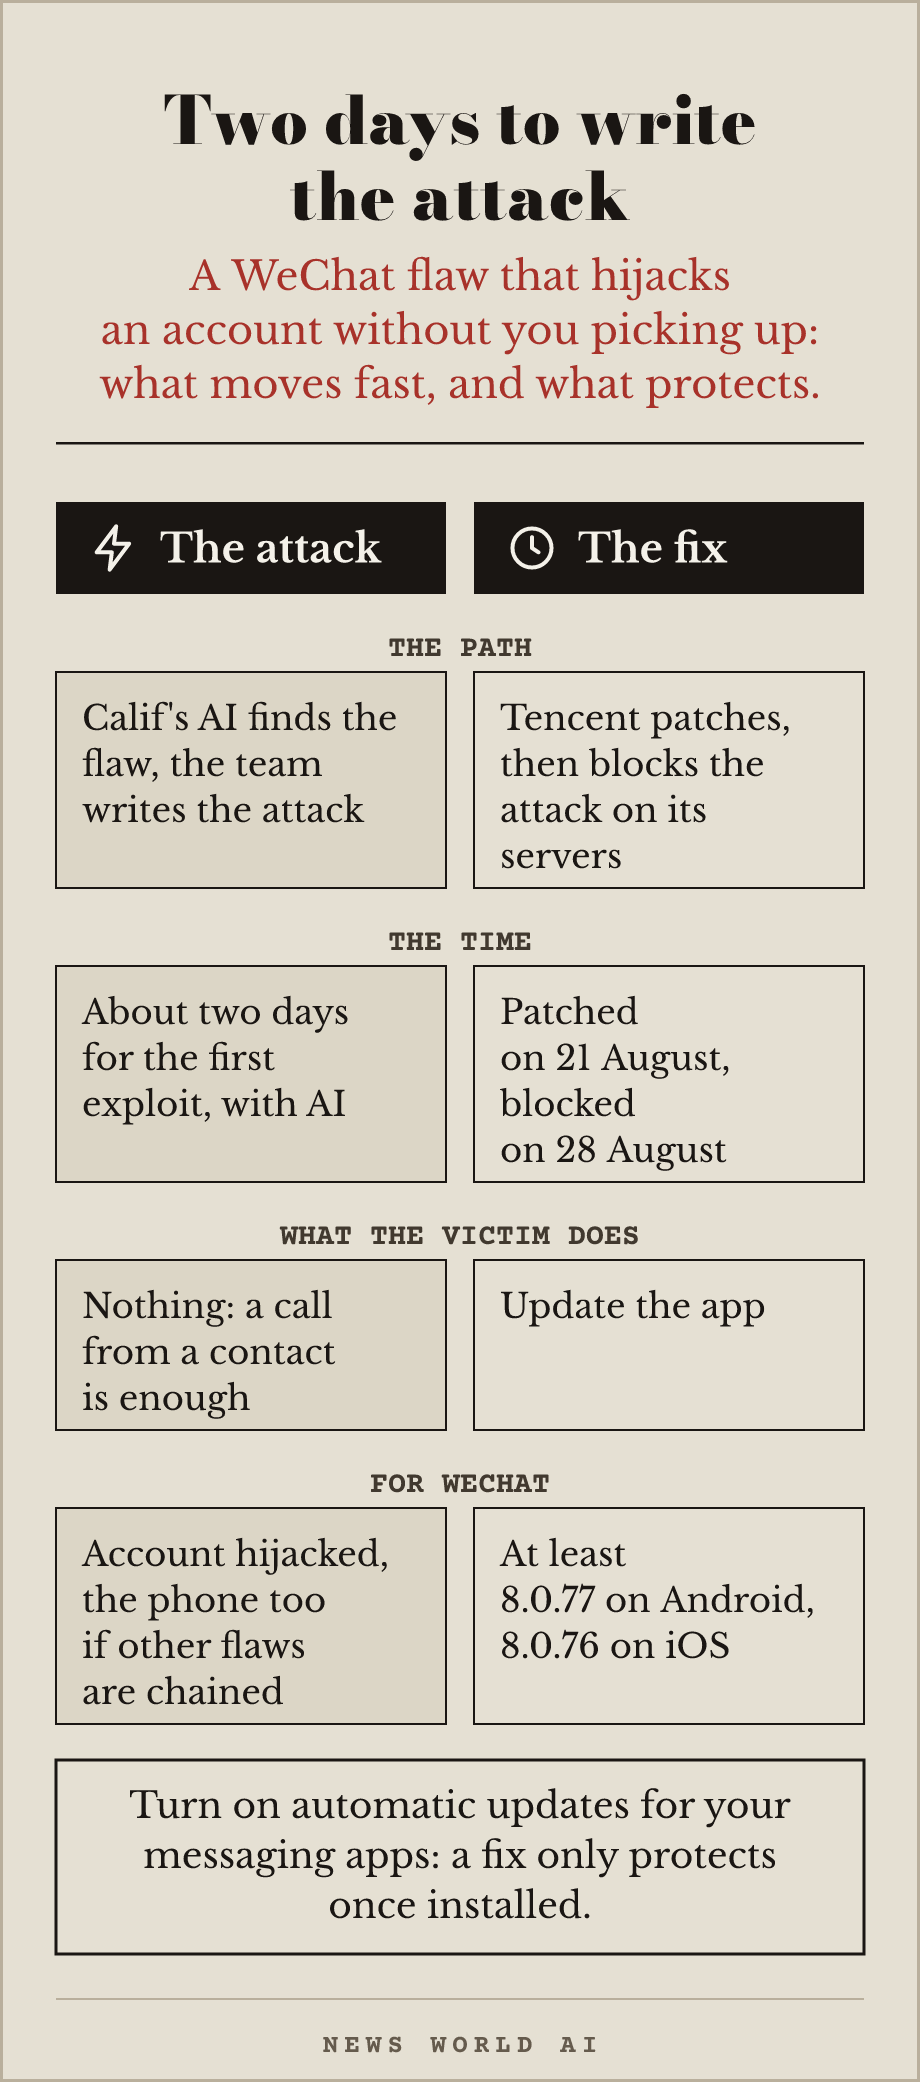
Calif published WeWorm on September 8: a demo worm built on a WeChat flaw that needs no action from the victim, on iOS and Android. A call from a contact is enough to hijack the victim's WeChat account, even if they do not pick up (declining the call stops the attempt); chained with other flaws, the attack can take over the phone. Calif's AI found the flaw in July, then the team wrote the first exploit in about two days with its help, and the worm in a week. Tencent shipped the fix on August 21.
The right move. Turn on automatic updates for all your messaging apps, today. For WeChat, check that you run at least version 8.0.77 on Android or 8.0.76 on iOS: according to Calif, Tencent has also been blocking the attack on its servers since August 28.
Reply to this email and tell us what you are building. Every reply is read.
— News World AI
Get the newsletter
Every Tuesday, in four minutes: what shipped in AI and what you can actually try the same day.
Double opt-in by email. One-click unsubscribe, link in plain sight in every issue.
Geneva, Switzerland. Write to hello@newsworldai.xyz.