News World

Artificial Intelligence
Infographic 2 minutes

LiteLLM: the made-up token that opens your tools
LiteLLM: the made-up token that opens your tools
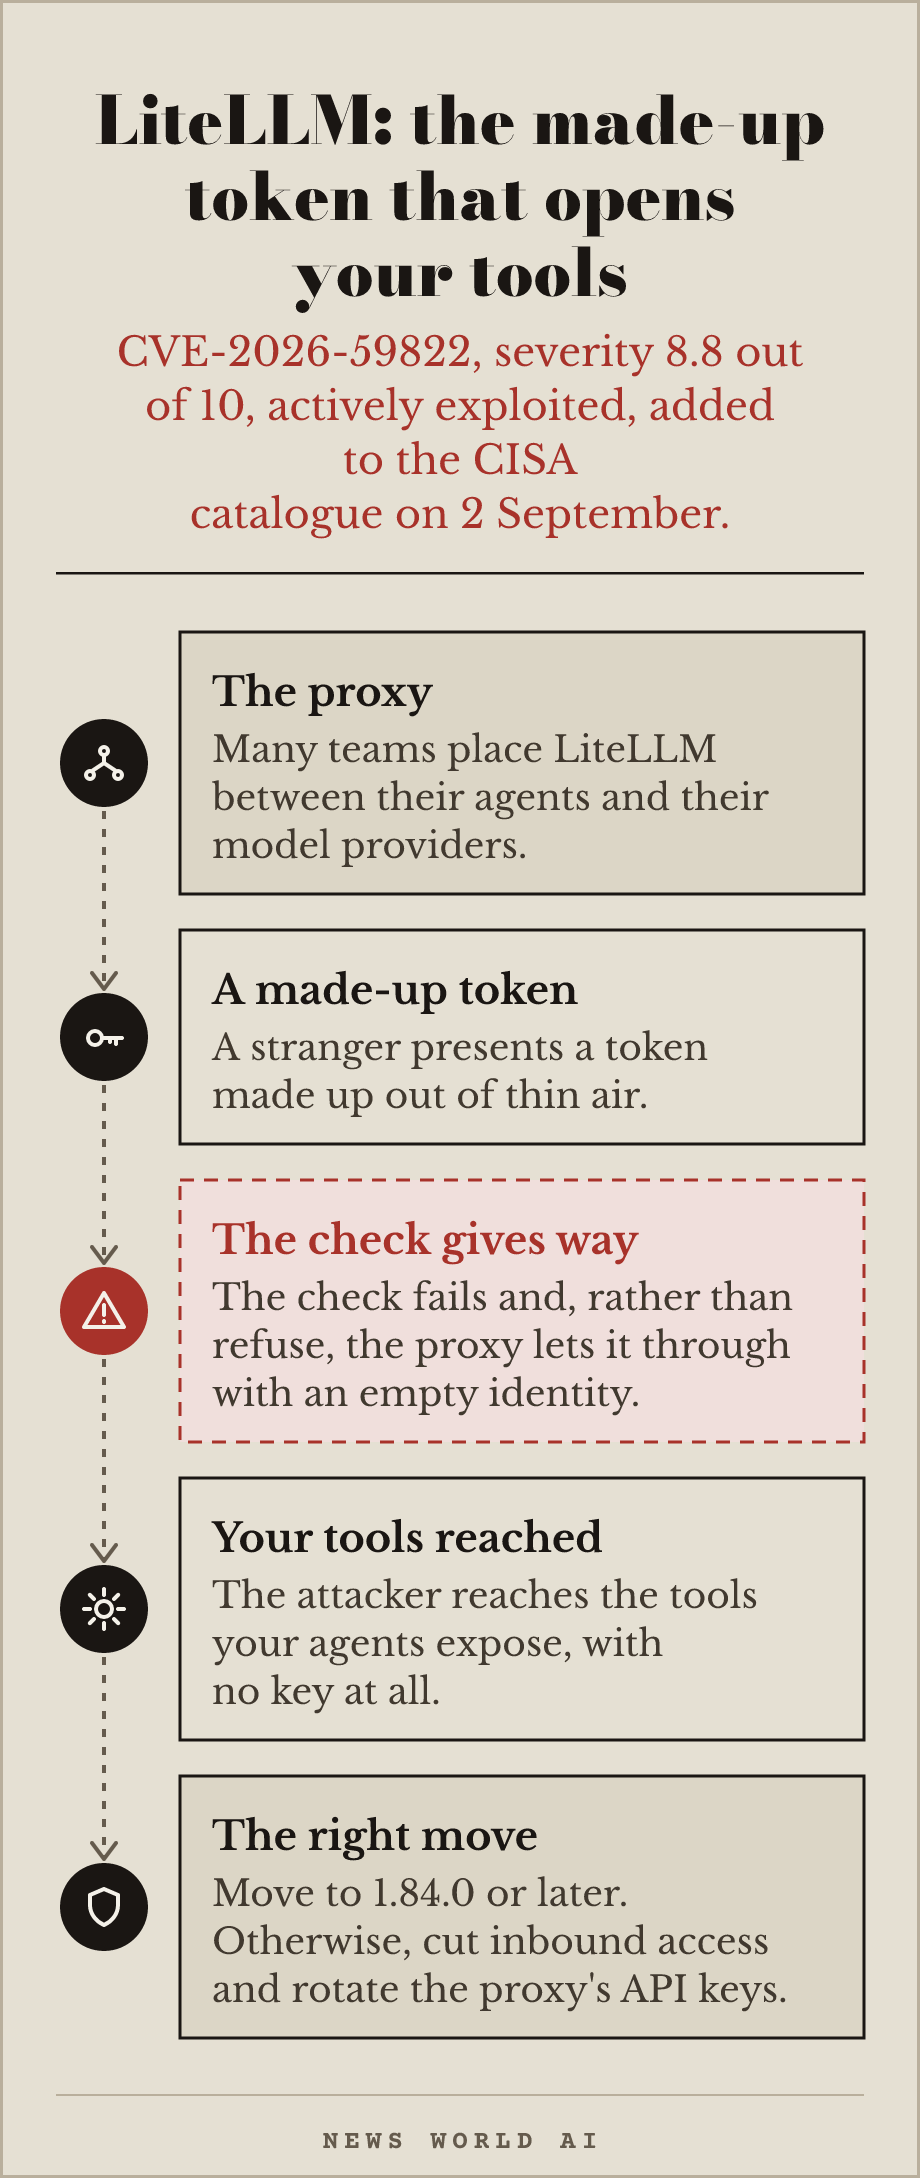
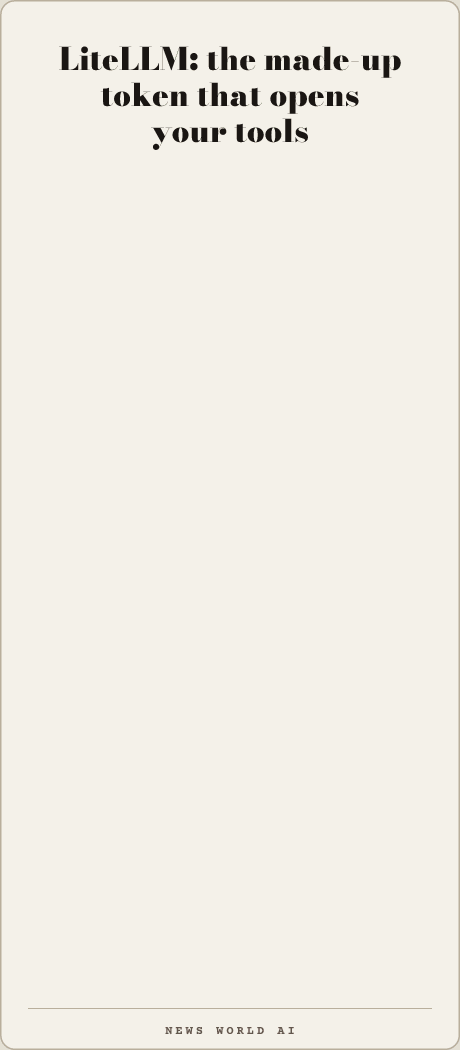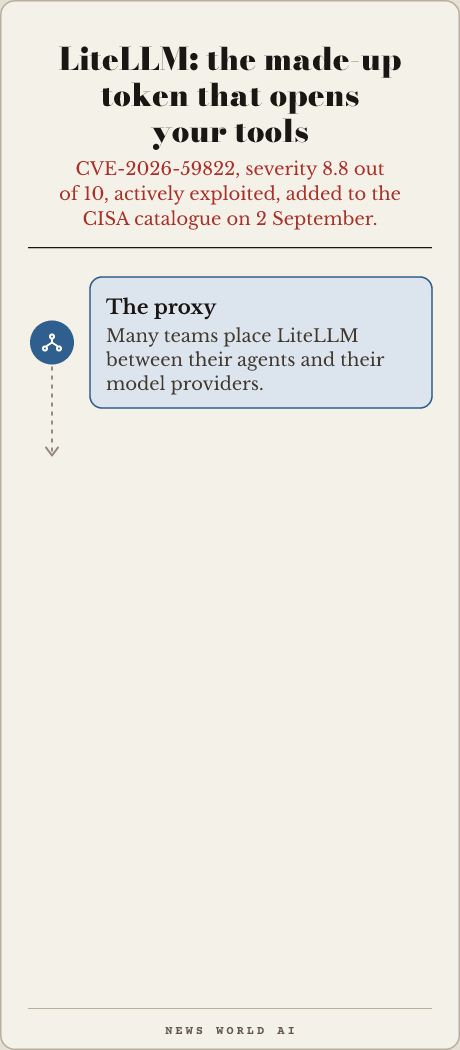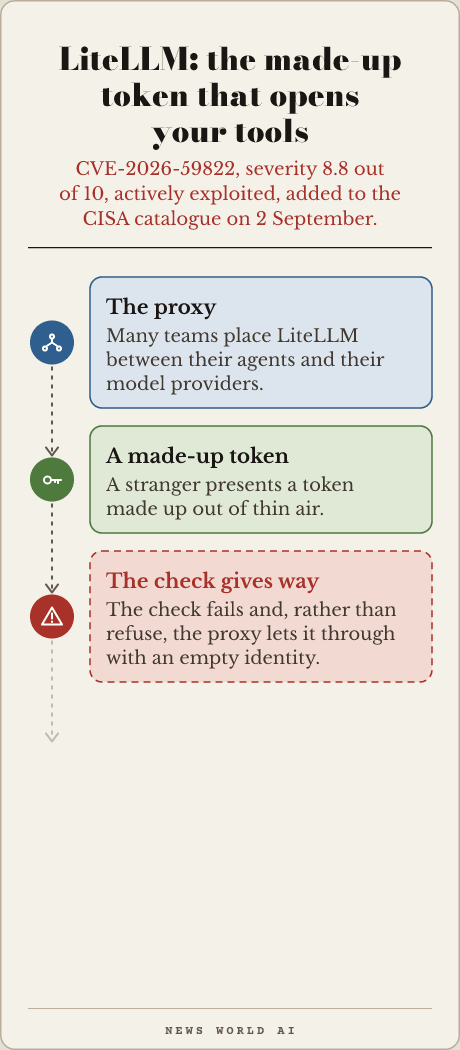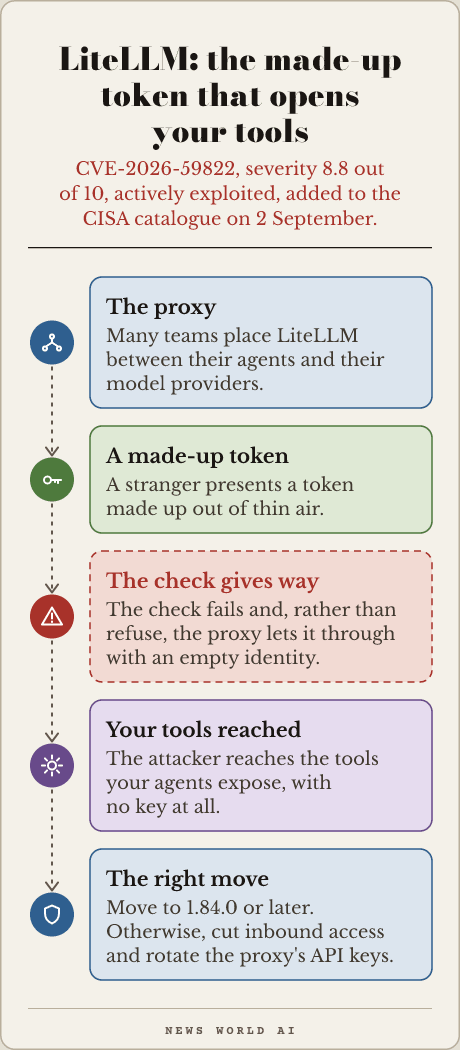
LiteLLM: the made-up token that opens your tools. CVE-2026-59822, severity 8.8 out of 10, actively exploited, added to the CISA catalogue on 2 September. The proxy. Many teams place LiteLLM between their agents and their model providers. A made-up token. A stranger presents a token made up out of thin air. The check gives way. The check fails and, rather than refuse, the proxy lets it through with an empty identity. Your tools reached. The attacker reaches the tools your agents expose, with no key at all. The right move. Move to 1.84.0 or later. Otherwise, cut inbound access and rotate the proxy's API keys.

Share on LinkedIn

Download the animated GIF to post it as is on a social network, or the still image (PNG).
From issue 002, section « The security reflex ».

Infographic

Get the newsletter

Every Tuesday, in four minutes: what shipped in AI and what you can actually try the same day.

Double opt-in by email. One-click unsubscribe, link in plain sight in every issue.

News World AI

Geneva, Switzerland. Write to hello@newsworldai.xyz.